More than a million Android devices served criminals through their own firmware. Digital signage hardware was among the infected devices.
Cybersecurity: Google Takes Down Global Android Botnet
Google, Japanese police and five companies have detected, exposed and shut down a global botnet. Partners included Lumen, Synthient and Trend AI.
The network, called XCPE, comprised more than 1.3 million Android devices. Besides TV boxes, digital signage devices were also infected, according to Google’s report. Google gave no further details on numbers or models.
Google blames Shenzhen-based manufacturer Videostrong. The company allegedly built a backdoor, a hidden remote access point, into its own firmware. According to Google, Videostrong sold that access to criminals. They routed third-party traffic through the devices’ internet connections and faked ad views. Videostrong is now banned from building certified Android devices.
Devices affected worldwide
Security provider Trend AI counted about 1.47 million infected devices from June to early October. Most are in Malaysia, Brazil, Iraq, Mexico and Taiwan. Germany, the U.S., the U.K., Australia and Canada each had roughly 26,000 to 42,000.
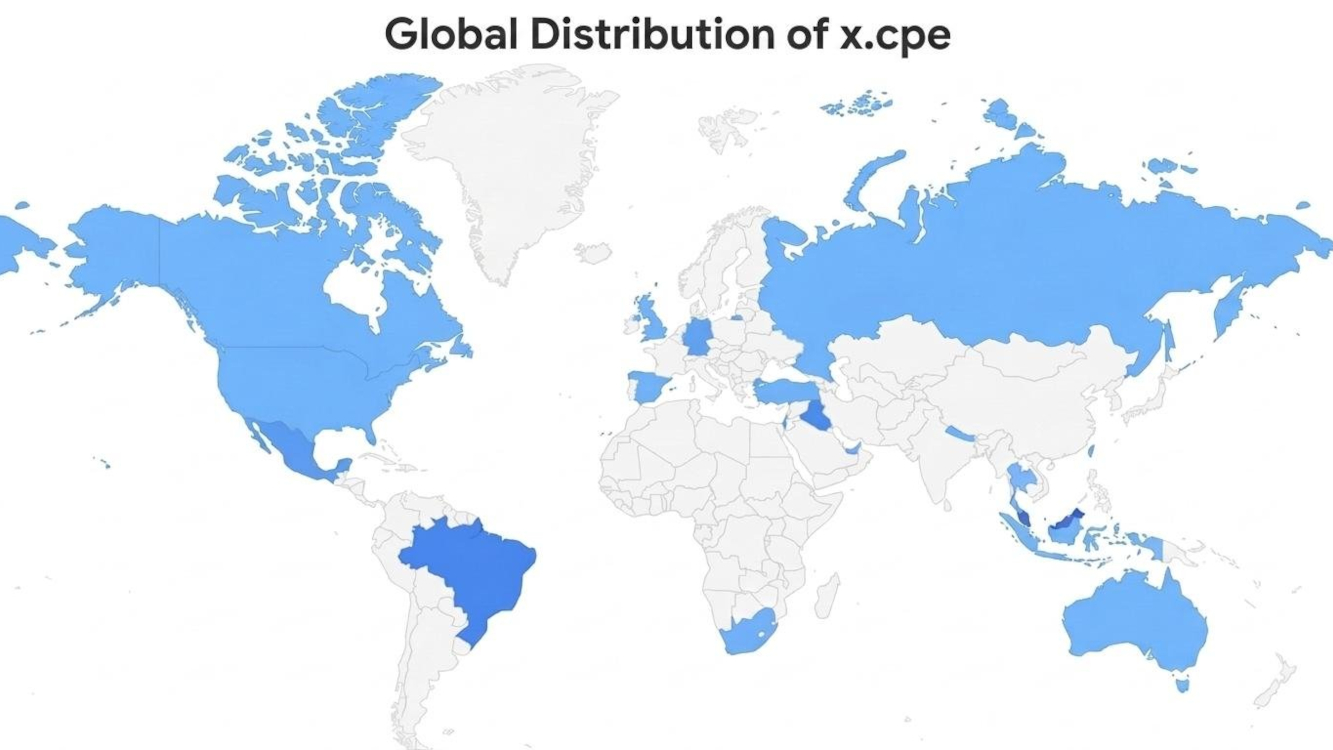
Trend AI says the actual numbers are likely higher. Google’s world map, which has no legend, shows the United States among the few shaded countries such as Canada or Germany.
What operators should check now
Network operators and integrators using low-cost Android boxes or white-label hardware should check first. Android certification alone is not sufficient proof. Partner Plume says the backdoor also hit certified devices. Synthient found it on Mecool-branded boxes and published 182 suspicious model names.
According to Synthient, a model name alone does not prove infection. Operators can search their firewall logs for the domains and IP addresses listed in Google’s report.
The command servers are offline, but the backdoor remains in the firmware. If deleted, it reinstalls itself on reboot. According to Trend AI, only action by the manufacturer or platform, or replacing the devices, will help. The partners advise taking suspicious devices offline.
Firmware origin becomes an issue
Smart devices should also run on separate network segments. A compromised player can serve as an entry point to the corporate network. According to Google, retailers and distributors should require independent security audits from contract manufacturers.
Google’s intervention shut down the botnet, but the question of where the firmware comes from remains with operators. For digital signage, security is becoming a supply chain issue.